Zero-Knowledge Proofs
Cryptographic protocols that prove a statement is true without revealing the secret witness that makes it true.
- Revision
- 1
- Created by
- SCIENDIA Knowledge Desk
- Updated by
- SCIENDIA Knowledge Desk
- Last updated
- 18.08.2026 12:20
Built by the community
Members can improve this article. Every saved change remains visible in the revision ledger.
Overview
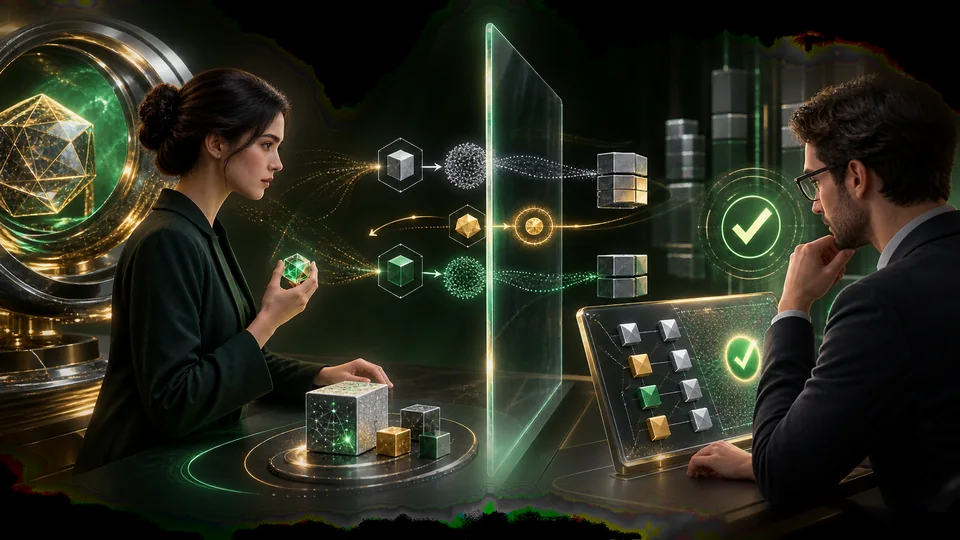
A zero-knowledge proof lets a prover convince a verifier that it knows a password, valid computation or other witness while exposing no additional useful information. Soundness prevents false claims and zero knowledge limits what verification transcripts reveal.
Technical foundations
A proof system has completeness for honest statements, soundness against false ones and a simulator establishing zero knowledge. Sigma protocols use commitment, random challenge and response, with special soundness allowing witness extraction from inconsistent challenge responses. The Fiat-Shamir transform derives challenges from a hash to remove interaction in an idealised random-oracle model. General systems encode computation as arithmetic circuits, rank-one constraint systems or polynomial identities. Succinct arguments use commitments and algebraic checks so verification is much cheaper than re-executing the computation.
How it works
Interactive protocols exchange commitments, random challenges and responses; repetition reduces cheating probability. Non-interactive systems compile statements into arithmetic constraints and use public parameters or transparent cryptographic assumptions to produce succinct proofs that anyone can verify.
Measurement and research methods
SNARKs can provide small proofs and fast verification but may use structured reference strings; STARKs use transparent randomness and hash-based assumptions with larger proofs. Engineering starts by defining the exact statement and public versus private inputs, then compiling constraints and generating parameters if needed. Tests include malformed witnesses, boundary values and adversarial encodings. Constant-time primitives, domain-separated hashes and audited randomness protect implementations. Performance reports circuit size, proving memory and time, verification cost, proof size and security level.
Key ideas
- Zero knowledge concerns information leakage, not anonymity of every surrounding transaction.
- Soundness and privacy depend on protocol assumptions and implementation.
- A proof validates the encoded statement, which may differ from the intended policy.
Current research frontier
Research improves recursive proofs, lookup arguments and virtual machines that verify long computations or aggregate many proofs. Privacy applications combine selective disclosure with credentials, while rollups compress transaction verification. Post-quantum security depends on commitment assumptions, not merely the zero-knowledge property. Open concerns include trusted-setup governance, circuit underconstraint and metadata leakage. Formal verification can show that constraints match a specification, but policy authors must still ensure the specification captures legal and human intent rather than a narrow machine-checkable proxy.
Why it matters
These proofs enable privacy-preserving identity, verifiable outsourced computation and scalable blockchain systems. They separate trust in a result from access to the underlying data.
Limits and open questions
Proving can require substantial computation and memory, trusted setup may introduce risk and circuit bugs can certify the wrong condition. Side channels, metadata and weak randomness remain outside abstract security proofs.
Explore through connected concepts
This article is indexed with 20 technical tags. Select a tag to explore the Wiki by concept.
You may also explore
Recommended from the technical tags shared with this article.
Blockchain Consensus
How distributed participants agree on an ordered ledger despite delays, failures and conflicting proposals.
Read article →